SBI confirms customer data exposed on dark web
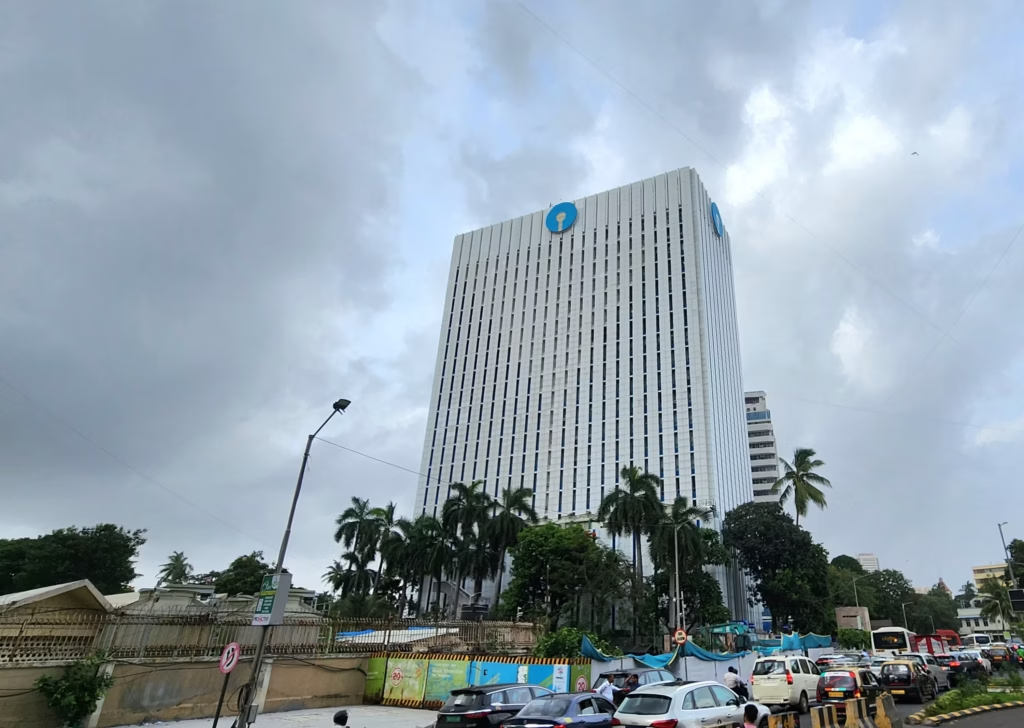
The State Bank of India disclosed in a stock-exchange filing on 21 October that personal data of some customers was exposed on the dark web. This followed alerts it received on 16 October, including from CERT-In. A preliminary review of about 3.75 lakh leaked records found 3,897 containing personally identifiable information.
Practice 2 MCQsMains
Why in news
A threat actor had claimed on a dark-web forum to hold about 3.75 lakh rows of SBI-linked data and 2,722 PDF files, mostly loan-related. SBI has appointed a CERT-In-empanelled agency to establish the source and authenticity of the data.
Prelims pointers
- Exposed fields include mobile numbers, dates of birth, names, email and home addresses, Customer Information File (CIF) identifiers and loan-lead metadata.
- CERT-In works under MeitY and is the national nodal agency for cyber incidents under Section 70B of the IT Act, 2000.
- CERT-In's 2022 directions require cyber incidents to be reported within six hours of noticing them.
- The Digital Personal Data Protection Act, 2023 requires data fiduciaries to report personal-data breaches to the Data Protection Board and to affected individuals.
- Under the DPDP Act, failure to take reasonable security safeguards can attract a penalty of up to ₹250 crore.
- The right to privacy is part of Article 21 (K.S. Puttaswamy, 2017).
Mains angle
Banks hold some of the most sensitive data in the economy. Leaks of loan and KYC data feed phishing and identity fraud, and test how quickly data-protection law is enforced.
6